AWS workloads need continuous monitoring since AWS secures infrastructure, but you are responsible for protecting your servers
MaxProtect provides 24/7 protection, threat detection, and vulnerability management.
001.
Misconfigured security groups, open SSH access, and public services can expose servers to unauthorized access.
002.
Outdated packages and operating systems create vulnerabilities that attackers exploit through malware, ransomware, and other threats.
003.
Lack of centralized monitoring and excessive security alerts make it difficult to detect and respond to real threats in time.
Under AWS’s shared responsibility model, AWS protects the infrastructure that runs its services: the data centres, hardware, network and hypervisor. Everything you put on an EC2 instance is your responsibility. That includes the operating system and its patches, user accounts and SSH keys, the security group rules you open, the software you install and the logs that show who did what.
That’s where most AWS breaches actually happen: an unpatched package, an SSH port open to the world, a reused password or malware running quietly on an instance. MaxProtect focuses on that layer, the operating systems and workloads attackers actually target, and runs it for you around the clock.
MaxProtect provides continuous monitoring, threat detection, vulnerability management, endpoint protection, and security hardening to fully secure AWS environments.
Monitor servers, applications, processes, user activity, and system events around the clock to identify suspicious behavior before it becomes a security incident.
Detect indicators of compromise, privilege escalation attempts, malware activity, unauthorized access, and abnormal behavior across AWS workloads.
Identify outdated packages, missing patches, insecure configurations, and known vulnerabilities that increase your attack surface.
Analyze logs and security events across AWS instances to detect hidden threats while implementing security best practices to reduce attack surfaces and strengthen overall system resilience.
We provide a detailed monthly report showing exactly what we blocked, what we patched, and the current health of your infrastructure.
| Risk on your instance | What MaxProtect does |
|---|---|
| SSH, RDP or database ports open to the internet | We review your security groups and access permissions, enforce key-based SSH authentication and close ports that don’t need to be open. |
| Missing OS and kernel patches | Managed patching: we apply targeted kernel and core-service updates during your maintenance window. |
| Weak default configuration | Managed hardening against CIS Benchmarks: strict access controls, legacy services retired and a minimal attack surface. |
| Malware, ransomware and fileless attacks | Our behavioral endpoint protection agent detects and blocks malicious activity in real time. |
| Suspicious logins and privilege escalation | Our 24/7 human-led SOC monitors system events and logs, investigates anomalies and filters out false alarms. |
| New vulnerabilities appearing over time | A monthly vulnerability scan and report showing what we blocked, what we patched and what’s left to fix. |
This covers Linux (Ubuntu, CentOS, RHEL, AlmaLinux) and Windows Server instances. See how our Linux server security monitoring works.
AWS offers strong native security services, and many teams already use some of them:
These services are good at raising findings. MaxProtect adds a hands-on layer inside your instances: we harden the operating system, manage patching and have human analysts watching your servers 24/7. Our guide to cloud security monitoring explains why.
Here’s what that looks like in practice:
Most cloud security providers focus primarily on cloud platforms.
MaxProtect focuses on the operating systems and workloads attackers actually target.
Our team specializes in Server security monitoring, vulnerability management, endpoint protection, and security operations for cloud-hosted infrastructure.
A security plan that fits your business size and protection requirements.
Includes:
See exactly where your servers stand. No credentials required.
⚠️ Audit Eligibility: This audit is specifically designed for Dedicated Servers, VPS, or Cloud Instances. We cannot perform audits on “Shared Hosting” accounts unless you are the owner/administrator of the entire physical or virtual server.
The document outlines actionable mitigation strategies and technical recommendations to strengthen defenses against unauthorized access and cyber threats.
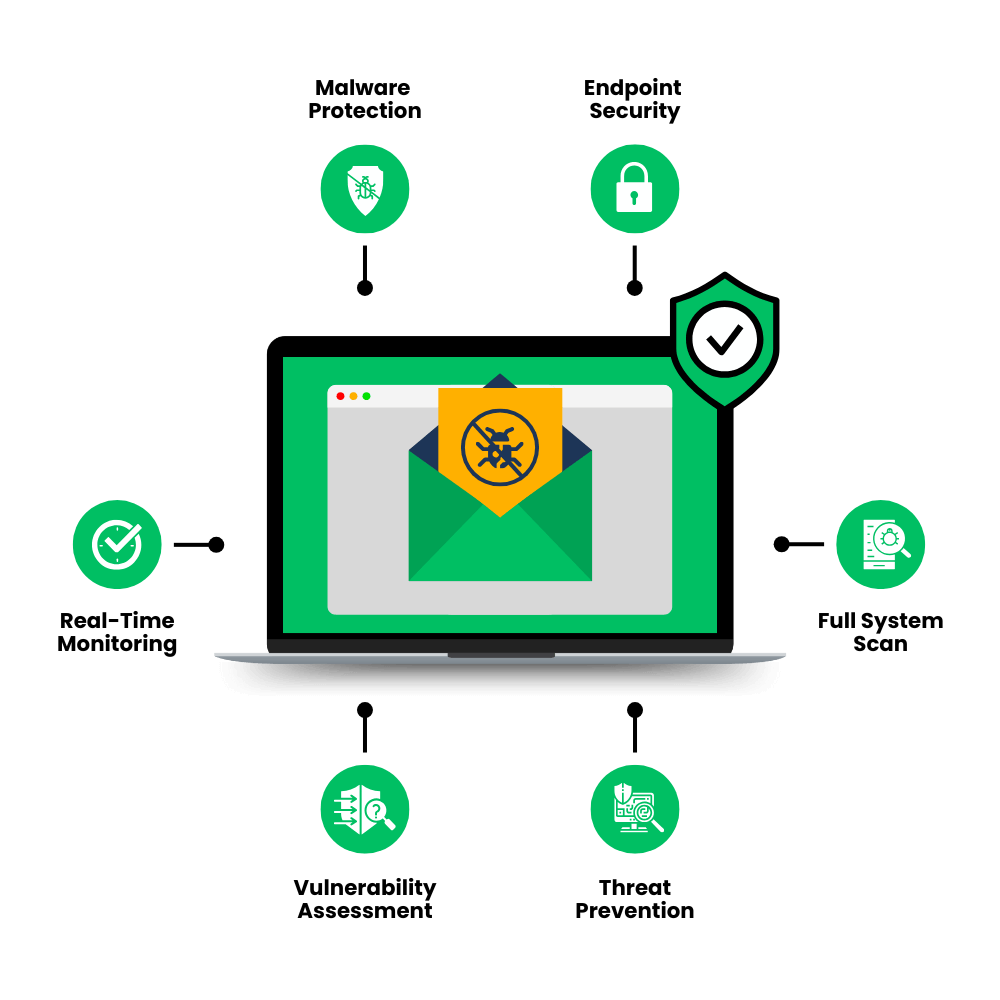
AWS secures the infrastructure underneath your instances, but under the shared responsibility model the operating system, patches, user accounts, security group rules and the software you run are your responsibility. MaxProtect takes on that layer for you: hardening, patching, endpoint protection and 24/7 SOC monitoring.
$100 per server per month. That covers 24/7 SOC monitoring, our endpoint protection agent, a monthly vulnerability scan and report, managed patching and unlimited security incident support. Hosting providers and large fleets can ask about our custom white-label SOC plan.
Kubernetes and container workloads are part of what we protect on AWS. We harden and patch the underlying servers and monitor them 24/7, which matters because every container shares its host’s kernel.
No. Our endpoint protection is built for high-uptime environments. It blocks malware and ransomware in the background without causing system latency or requiring unnecessary reboots.
Yes. The free external assessment works on cloud instances, including AWS. We run it from outside with no credentials and send you a PDF report of open ports, exposed services, SSH configuration gaps and high-priority vulnerabilities, each with mitigation steps.